
Table of Contents
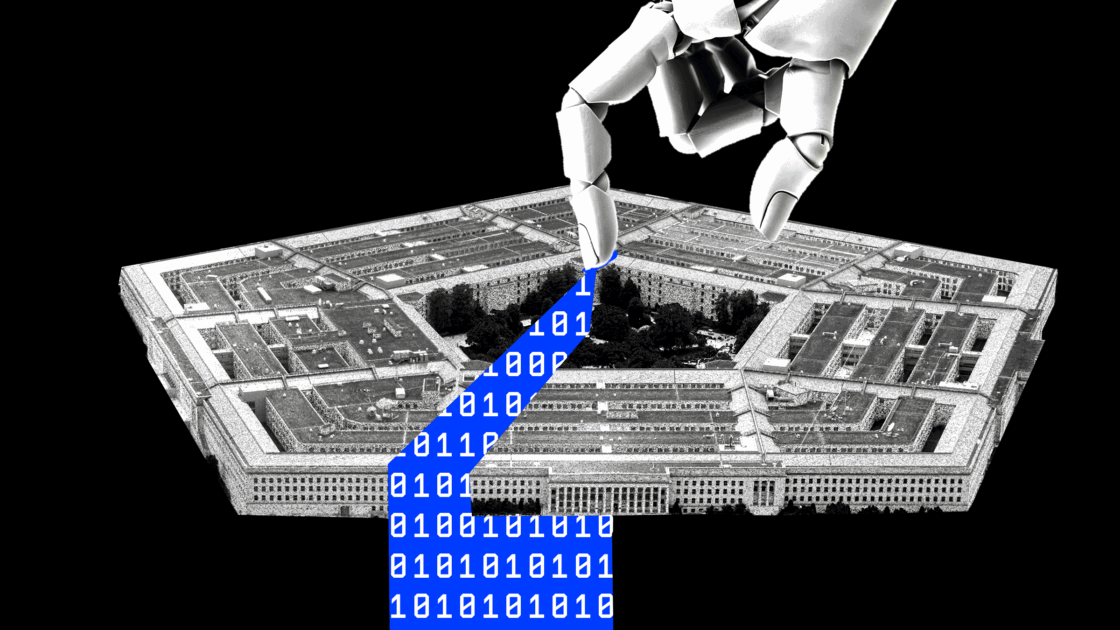
A contractor working for defense firm Accenture connected an unauthorized personal artificial intelligence agent to a secure Department of Defense network, exposing sensitive government information for two months before the flaw was detected and patched. The security breach involved the Non-classified Internet Protocol Router Network (NIPRNet), a heavily guarded system used to manage sensitive military and infrastructure data.
Security Compromise and Data Vulnerabilities
To automate code generation and deploy cloud servers, the Accenture employee provided their login credentials to an AI agent running Anthropic’s Claude LLM. According to sources who spoke to WIRED, this granted the agent administrative access, allowing it to bypass standard network authentication and security controls. The AI tool connected to the internet to perform its tasks, inadvertently sending login credentials, passwords, and a structural map of NIPRNet to an external website.
The affected system handles Controlled Unclassified Information (CUI), which includes data regarding nuclear submarine propulsion, critical infrastructure vulnerabilities, emergency response plans, and designs for military and space technology. Although individual data points on the network may be unclassified, security experts note that aggregating such information can effectively yield classified intelligence. A source familiar with the incident told WIRED that allowing third-party software into the network creates “100 percent a national security threat and could cause irreparable harm.”
Responses and Failure to Report
A Department of Defense spokesperson told WIRED that “the Department does not comment on the status of its networks or systems.” Meanwhile, an Accenture spokesperson stated that the allegations were “thoroughly and independently investigated and found to be without merit” and that the company had “fully complied with our legal and contractual obligations.” Accenture did not specify who conducted the investigation nor did it deny that an incident occurred.
Anthropic’s usage policies explicitly prohibit using its systems to “interfere with the operation of military bases and related infrastructure” or to “bypass security controls such as authentication systems, end point protection, or monitoring tools without authorization.” Defense personnel are currently banned from using Claude. Furthermore, federal contractors are mandated to report cybersecurity incidents within 72 hours of discovery, but sources indicated Accenture did not initially disclose the breach to the government.
Accenture holds over $3.5 billion in active federal contracts, including nearly $605 million with the Department of Defense. The incident comes shortly after the Federal Bureau of Investigation removed an Accenture contractor in early October for failing to fix a security flaw, which permitted the hacking group ShinyHunters to compromise personal details belonging to thousands of FBI employees.
Broader National Security Implications
Jake Williams, a former National Security Agency hacker and faculty member at IANS, explained to WIRED that software tools developed on NIPRNet are often transferred to classified, air-gapped networks like the Secret Internet Protocol Router Network (SIPRNet) or the Joint Worldwide Intelligence Communications System (JWICS). Williams warned that malicious code or backdoors inserted into NIPRNet through stolen credentials could potentially be deployed into these higher-security systems undetected, as automated security scanning tools frequently fail to identify logical backdoors.
Matt Triner, founder of IT consulting firm Hunter Strategy, pointed out that federal contractors face structural disincentives regarding transparency. Contractors risk losing lucrative government accounts if they disclose network breaches, creating tension between reporting requirements and commercial interests. Triner added that growing pressure on contractors to deliver code rapidly with lower budgets further exacerbates cybersecurity risks as automated “vibe coding” practices gain traction.
This is not the first instance where third-party coding practices have raised concerns within defense operations. Previous reporting revealed that Microsoft utilized American staff with security clearances to oversee code written by outsourced personnel in foreign nations, a practice experts warned left potential openings for undetected vulnerabilities in government infrastructure.